Banking-Grade AI Code: The 9-Layer Security Pipeline
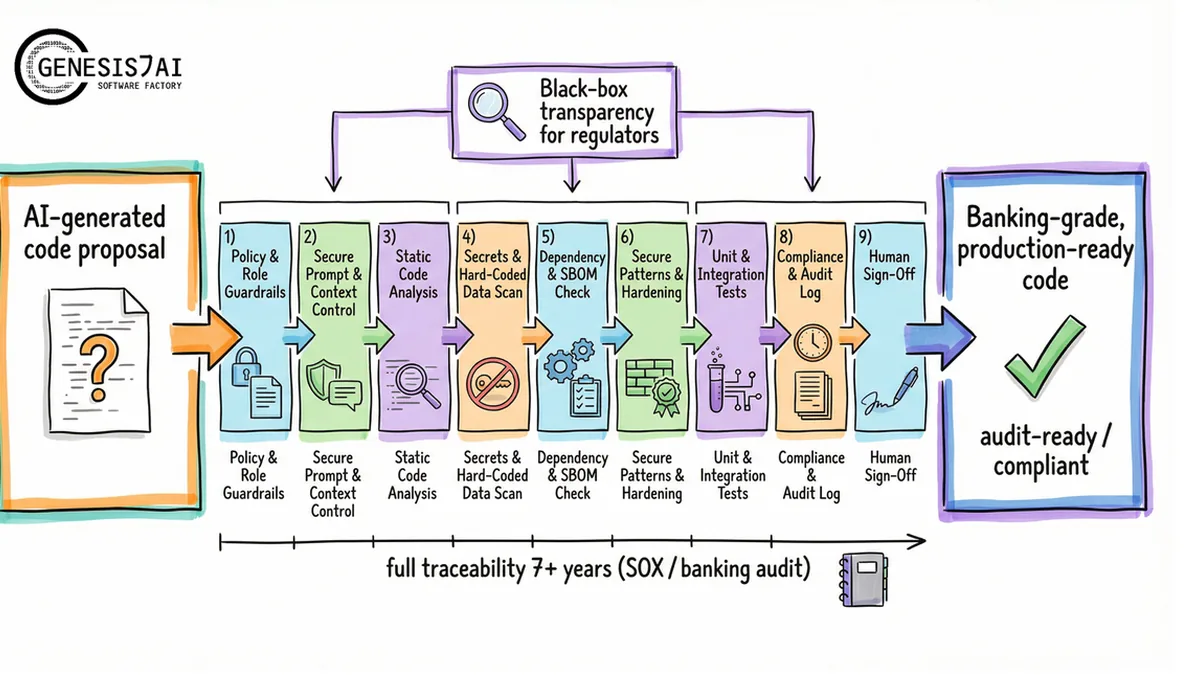
Black-Box Transparency: How Multi-Layer Validation Enables Regulatory Trust
Article illustration
The Black-Box Challenge: Why Generic AI Fails Audit Requirements
Traditional AI coding assistants operate as regulatory black boxes. GitHub Copilot generates code through neural network transformations, providing no explanation of security decisions, no compliance mapping, and no audit trail of validation steps. The model generates code based on patterns learned from public repositories - 39% of which contain vulnerabilities, according to a 2024 Gartner analysis - with no mechanism to verify SOX segregation of duties, PCI DSS secure coding standards, or DORA change management requirements.
This opacity violates banking audit principles. SOX requires documented internal controls over financial systems. DORA Article 9 mandates documented change management with recorded testing, assessment, approval, implementation, and verification. PCI DSS Requirement 6.2 requires evidence of secure development practices. Generic AI assistants provide none of this documentation - no audit trail captures why specific code patterns were chosen, which security controls were considered, how code maps to compliance requirements, or whether vulnerabilities exist. The 6.4% secret leakage rate in AI-enabled repositories - 40% higher than average - demonstrates how black-box AI introduces compliance risks.
The 9-Layer Security Pipeline: Defense in Depth
Purpose-built AI platforms resolve the black-box problem through nine independent validation stages, each generating audit evidence.
Black-Box Transparency: Architecture for Trust
The platform operates through specialized AI agents (coordination, requirements, security, generation, validation, testing, documentation, approval) communicating through a central knowledge graph that maintains structured relationships between code patterns, security controls, regulatory requirements, and validation results.
Critical distinction: while AI models operate as neural networks (inherently black boxes), the platform architecture provides complete transparency through validation layers. Every security decision, compliance mapping, and validation result generates audit evidence. Code generation transforms from an opaque transformation into a documented, verifiable, auditable workflow.
Integration with enterprise security tools occurs through standardized APIs: SonarQube scans via REST API, Snyk dependency scanning, and OWASP ZAP dynamic testing. Approval workflows integrate with enterprise identity management (Active Directory, Okta, Azure AD), enforcing role-based access controls and segregation of duties. All validation results, approval actions, and deployment events are logged to immutable audit trails using blockchain or tamper-proof storage, ensuring seven-year SOX retention with cryptographic verification.
Strategic Conclusion: Architecture as Competitive Advantage
Banking cannot accept black-box AI code generation. Regulatory requirements demand comprehensive documentation, independent validation, and tamper-proof audit trails. Generic AI assistants designed for productivity rather than compliance create banking compliance challenges rather than resolving them.
The 9-layer security pipeline demonstrates how purpose-built platforms transform AI code generation from an opaque productivity tool into a transparent, auditable, compliant software development platform. Organizations implementing multi-layer validation achieve zero critical vulnerabilities on first-pass generation, a 60-75% reduction in compliance overhead through automated documentation, and an 80% acceleration in audit preparation through native audit trail generation.
Technical architecture determines regulatory viability. Organizations selecting AI platforms based on productivity metrics rather than compliance architecture face extensive manual documentation overhead and regulatory risk. Those implementing compliance-first architectures with multi-layer validation redirect compliance resources to innovation while establishing structural advantages that competitors cannot rapidly replicate.
Technical Recommendation
Evaluate AI code generation platforms based on architectural transparency - the number of independent validation layers, compliance pattern library coverage, audit trail automation, and enterprise security tool integration. Demand proof of zero critical vulnerabilities on first-pass generation and comprehensive documentation auto-generation supporting SOX, PCI DSS, and DORA audit requirements.