Minimum Sufficient Sovereignty: Why Your Company Doesn't Need Full AI Sovereignty, but Without a Certain Minimum It Will Perish
On the other hand, organizations that ignore sovereignty altogether accumulate risks that they do not see on a daily basis, but which materialize suddenly - during a regulatory audit, a geopolitical incident, or a change in the terms of a contract with a supplier. There are five types of such risks:
- Regulatory complexity (US CLOUD Act, EU AI Act, data localization)
- Technical disruptions (geopolitics affects service continuity)
- IP and data ownership (governments access data even when stored abroad)
- Economic exposure (customs duties, exit taxes, migration costs)
- Reputational risk (lack of transparency in data management)
Four Dimensions of Sovereignty and What You Really Need to Control
Before we move on to workload classification, it is important to understand that AI sovereignty is not a binary concept: there are four independent dimensions:
- Territorial - where the data and computing power are physically located
- Operational - who manages and secures the data and infrastructure
- Technological - who owns the technology stack and intellectual property
- Legal - which jurisdiction regulates access and compliance
An organization may be fully sovereign in the territorial dimension (servers in Poland), but completely dependent in the legal dimension (contract subject to Delaware law, US CLOUD Act). It is this invisible gap that is the most common source of problems in public tenders and NIS2 audits.
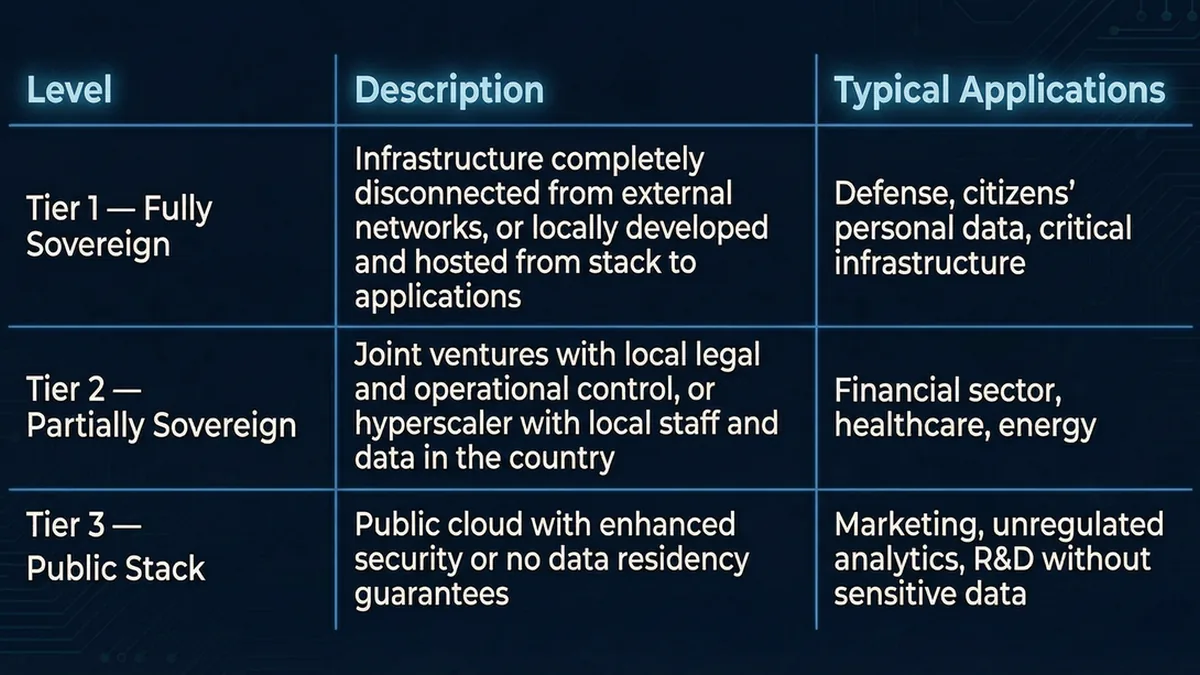
Three Levels of Sovereignty: How to Classify Your Workloads
Article illustration
5 Questions That CTOs/CIOs Should Ask Their Teams Today
Before you commission an external sovereignty readiness audit, answer these five questions honestly:
- Do you know which of your organization's data is subject to the US CLOUD Act - even if it is stored in a European data center of a US-based provider?
- Do you have full control over the encryption keys for data processed by AI systems, or do the keys reside with the provider?
- Are your AI models training or fine-tuning on production data sent to external APIs, and do you have legal and regulatory approval to do so?
- In the event of a geopolitical blockade or sanctions on a specific provider, could your critical processes operate for 72 hours without their services?
- Is your AI architecture portable - can you move workloads to another provider or on-premises within weeks, not months?
If you don't know the answer to any of these questions, you have a sovereignty gap that is already an operational risk today.
Case Study: Bank vs. Ministry - Two Different Responses to the Same Problem
Imagine two entities considering implementing an AI system for document analysis:
A commercial bank processes customer data covered by GDPR, DORA, and KNF recommendations. Its AI workloads can be divided into:
- Transaction analysis (Tier 2 - data in Poland, locally fine-tuned model)
- Customer service via chatbot (Tier 3 - pseudonymized data, global model acceptable)
- Scoring systems (Tier 1 - full sovereignty required by the regulator)
Three different workloads, three different levels of sovereignty - and none of them require rebuilding the entire infrastructure from scratch.
The ministry processes sensitive citizen data, classified documents, and critical infrastructure systems. Here, the answer is different: Tier 1 for everything that touches operational data, with Tier 2 only for productivity tools without access to sensitive data. But even in this case, you don't build your own graphics processors - technological sovereignty can mean hosting open-source models on your own infrastructure, not building them from scratch.
From Classification to Architecture: How It Works in Practice
Effective sovereign AI architecture defines so-called nonnegotiable control points: a set of control points that must be sovereign without exception:
- Data classification and permitted uses - what can leave the organization and what cannot
- Encryption and key ownership - who physically holds the keys, in which jurisdiction
- Identity, access, login, and monitoring - full auditability of AI model operations
- Model risk management and evaluations - built-in quality and security assessment mechanisms
- Incident response and lawful access paths - what happens when a regulatory or judicial authority requests access
This is not a list of product features. This is a list of architectural requirements that should be included in every RFP and every tender for AI systems in regulated organizations.
What This Means for Your Organization
Sovereign AI is not an infrastructure project; it is a strategic decision about where your control over your own intelligence ends. The good news is that you don't have to own everything. You need to know what you need to own - and make sure you have it. The rest can be hybrid, partnered, or even global.
The bad scenario isn't one where you use AWS or Azure. The bad scenario is one where you don't know what data is passing through them, who has legal access to it, and what will happen when geopolitics change tomorrow.
Want to see where your organization stands on the sovereignty map?
SAVANT-AI offers a Sovereign Readiness Audit - a structured assessment of four dimensions of sovereignty for your AI stack, culminating in a report with prioritized recommendations.