Vibe and Verify: A Practical Model for Combining AI Agents With Quality, Security, and Compliance in SDLC
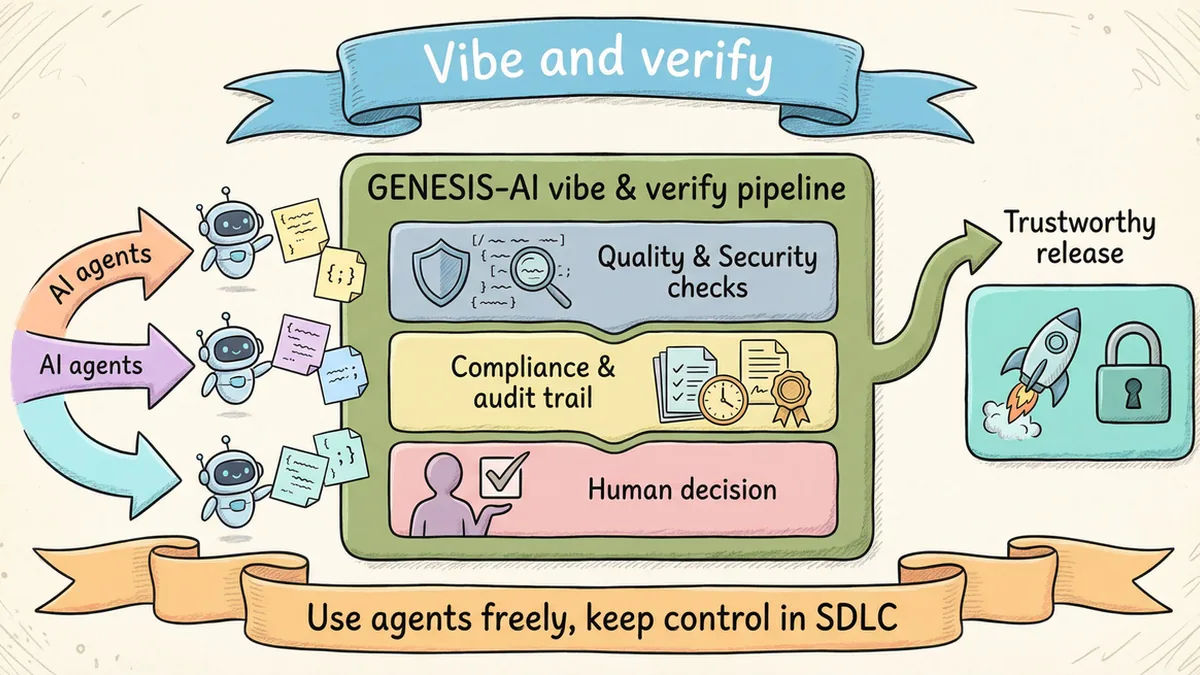
Vibe vs. Verify: What's the Real Issue?
Today's AI tools and agents can generate, refactor, and test large chunks of code. "Vibe" is easy: you type in a command, and a moment later you have a pull request ready to review. The hard part is "verify": how do you know that this code is secure, correct, and compliant with your organization's and regulator's requirements?
Article illustration
This tension is especially visible in large, regulated environments: banks, the public sector, and telcos. Code appears faster, but the risk of subtle errors, security vulnerabilities, or violations of internal rules increases. Instead of banning AI, you need guardrails around it: an architecture where the developer can freely "vibe," and the organization's system systematically verifies the result.
Step Zero: Define "Trustworthy Code" for Your Organization
Before you design guardrails, you must clearly answer: what does trustworthy code mean to us? In practice, it usually comes down to four dimensions:
- Security
- No obvious vulnerabilities.
- No data or secret leaks.
- Use of only approved libraries and services.
- Quality and maintainability
- Code is readable, consistent with company standards, and testable.
- Complexity is under control: you don't ship "spaghetti" just because AI suggested it.
- Compliance
- Industry and regulatory requirements are met.
- Internal policies are followed (logging, auditing, data retention, change structure).
- Explainability and repeatability
- You can show why code was accepted or rejected.
- The same fragment, passed through the pipeline, produces the same result.
Without such a definition, each team interprets "good code" differently. In the world of agents, that is a direct path to chaos and conflicts with security and compliance teams.
The "Vibe and Verify" Architecture: Layered, Not Ad Hoc
An effective way to think about this is as several successive layers that every code change must pass through.
Layer 1. Vibe: Agents Close to the Developer
This is the space for fast, exploratory work:
- An agent in the IDE suggests code, refactors, and generates tests.
- Background agents prepare pull requests for refactoring, modernization, or additional tests.
- The goal is to quickly produce a working proposal.
At this stage, you don't assume that the code is production-ready. You treat it as a draft that still needs to be verified.
Layer 2. Quality and Security: Guardrails With Rules + AI
Here, "verify" begins. A robust pattern is a combination of:
- Hard, deterministic rules: linters, style rules, security scanners, architectural rules.
- Specialized AI for code analysis: detection of non-obvious errors, anti-patterns, regressions, performance issues.
Key assumption: code is checked by a different layer than the one that generated it. You don't let the same model "grade itself." This helps you:
- Avoid blind spots of a single model.
- Explain the process to auditors ("this model writes, this other one - plus a set of rules - evaluates").
Layer 3. Compliance and Traceability: Shifting Control Left
AI accelerates coding, so if you leave compliance to the very end, you will hit problems faster instead of preventing them. Control needs to be shifted left - closer to where code is created.
In practice, this can mean:
- Defined system risk profiles (e.g., A/B/C) with different requirements for each.
- Automatic checks: only approved libraries are used; logging meets standards; accessibility rules (e.g., WCAG) are followed.
- Building an audit trail: linking code changes to requirements, tickets, architecture decisions, and test results.
This way, when someone asks, "Did AI break our procedures?" you can show logs of prompts and responses, logs of agent decisions (what they changed and why), and reports from verification layers.
Layer 4. Human-in-the-Loop: The Accountable Decision
After all automated layers, you still need a human who:
- Understands the business context and risks.
- Makes the final decision on merge or release.
- Gets involved in exceptional situations: conflicting signals, high risk levels, new regulations.
It is crucial to define clear criteria that trigger this intervention: for example, scanner results above a risk threshold, changes in critical modules, or lack of precedent for a given pattern. Without such criteria, human-in-the-loop becomes either a bottleneck or a pure formality.
The developer or architect is no longer an "AI proofreader line by line." They focus on what automation cannot see: business logic, customer impact, system architecture.
Guardrails in Practice: A Checklist That Actually Works
1. Classify Code by Risk
Not every part of the system needs the same rigor. A simple split:
- Low impact / low risk (scripts, internal tools): lighter verification path, more autonomy for agents.
- High impact / high risk (financial logic, settlements, critical systems): full "vibe and verify" path, more testing, independent verification, stronger human involvement.
This way, you don't block innovation where risk is low, while protecting the most sensitive areas.
2. Separate Generation and Verification
A principle that is easy to explain to security and regulators:
- One set of models/agents generates code.
- Another set - supported by rules - checks it.
This separation reduces the chance that a model misses its own errors and makes it easier to say, "we have independent control."
3. Write Down Your Definition of Trustworthy Code
It's worth having a document you can show to teams, auditors, and regulators, describing:
- Quality requirements for A/B/C systems.
- Security requirements (mandatory practices, prohibited patterns).
- Compliance requirements (logs, retention, traceability).
- Evidence required for code to be accepted (reports, logs, approvals).
You can then encode these rules into tools and agents instead of relying on informal agreements.
4. Measure Outcomes, Not "AI Magic"
Instead of boasting that "30% of code was written by AI," track:
- How time from ticket to implementation has changed.
- How the number of bugs and rollbacks has changed.
- How release quality has changed.
- What happens to backlog size and user satisfaction.
A common side effect: you speed up coding, but if you don't improve review, testing, and compliance, you just move the bottleneck elsewhere. End-to-end SDLC telemetry helps you spot this quickly.
How to Explain This in a Regulated Sector
Regulators and auditors usually care about two questions:
- Has AI lowered your standards for quality, security, and compliance?
- Can you demonstrate how the decision "this code is OK" was made?
You should be ready to answer:
- We keep the same or higher standards for AI-generated code as for handwritten code.
- We use a "vibe and verify" architecture with independent control layers.
- We maintain logs, reports, and a written definition of trustworthy code that can be reviewed and verified.
This shifts the conversation from "Is AI safe?" to "How exactly do you ensure safety and compliance when using AI?" - a discussion where you have strong arguments.
Where a Platform Like GENESIS-AI Fits
A platform such as GENESIS-AI can be the place where all layers of the "vibe and verify" model come together in a single coherent flow:
- You connect generating and verifying agents, plus quality, security, and compliance tools.
- You collect telemetry from the entire SDLC - from the first commit to production monitoring.
- You define and enforce trustworthy-code rules for different systems and customers, adjusting control levels to the risk profile.